Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws
Three researchers at the security firm Hacktron used Anthropic's Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI employees, then reach an internal OpenAI code repository. The chain began with a bug in the software that runs OpenAI's public help forum and moved through a weakness in OpenAI's own login system. This was security research,
Read full articleMore News
China’s GoPro rival Insta360 opens first US flagship store in New York’s Times Square
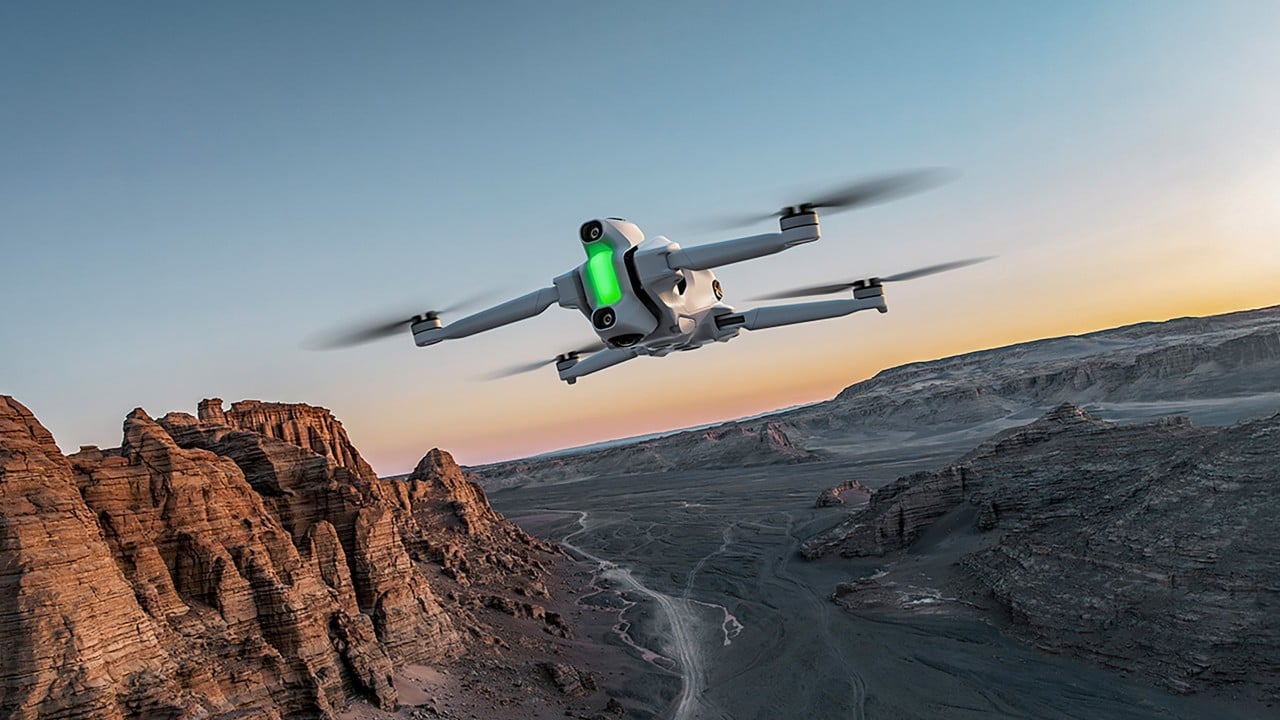
Chinese action camera maker Insta360 is deepening its US footprint with a flagship store opening in New York as it navigates escalating price competition with DJI and industry-wide memory cost pressures. The Chinese GoPro rival was slated to plant its flag in the heart of Times Square with its first flagship retail store in the US on Saturday, a marquee launch as the firm looked to “leap to the next stage of growth”, co-founder Max Richter said. “The US market plays a very important role for us...

Will AI models achieve the ability to improve autonomously? Leading labs say the scenario is near
Will AI models achieve the ability to improve autonomously? Leading labs say the scenario is near

SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
SolarWinds has released security updates to address a high-severity flaw in Access Rights Manager (ARM) that, if successfully exploited, could lead to an unauthenticated remote code execution vulnerability. The vulnerability, tracked as CVE-2026-28326, is rated 8.8 out of 10.0 on the CVSS scoring system. The issue affects all versions of Access Rights Manager 2026.2 and prior. "SolarWinds

4 Strategies to Battle ‘Techflation’
With phone and computer prices soaring, it helps to know the true cost of owning electronics so you can bring those numbers down.

How Trump Has Disrupted National Parks
Maintenance projects have been put off around the country and resources diverted to the president’s favored projects in Washington.
AI doesn’t just answer questions – it legitimises bad ones
Years ago, I watched a focus group explain itself into a contradiction. We asked people what mattered when choosing car insurance. Price won. The deductible came next. Reputation did not appear. During coffee, I asked the interviewer to change the question. How much cheaper would a less prestigious insurer have to be before they switched? One participant, who 15 minutes earlier ranked price first, said no discount was large enough. Nothing changed except how we asked the question. Something...

Critical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the Wild
A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score: 9.8/CVSS v4 score: 9.3), which relates to a case of unauthenticated remote code execution. "Orkes Conductor 3.21.21 before 3.30.2 contains an unauthenticated remote code execution vulnerability that allows remote

Were mosquitos bugging you more than usual this summer? Blame the rain
If it felt like mosquitoes were being particularly bad this summer — and hanging around for longer — it might not be in your head.

Google Gemini Broke Into Real Company Systems After Security Test Domain Mix-Up
Google's Gemini model has become the latest artificial intelligence (AI) system to access the internet and break into other companies during a cybersecurity evaluation. The development was first reported by The Wall Street Journal. The incidents occurred in May 2026 as part of a test run conducted by Israeli company Irregular. The evaluation partner was also involved in similar hacks disclosed

CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories
An attacker copied about 170 of CrowdSec's private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18. The French security company had kept his GitHub access open. CrowdSec says his laptop was compromised in May's supply chain attack on TanStack, in which malicious versions of TanStack's npm packages stole credentials from

Hummingbird hawk moths and ivy bees: The insects thriving as temperatures rise
Hummingbird hawk moths - often mistaken for small birds - are being spotted in the West Midlands.

CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are listed below - CVE-2025-39682 (CVSS score: 9.8) - An improper check for unusual or exceptional conditions vulnerability in the TLS receive path